AI is now embedded across technology management workflows, yet many organizations still lack clear, usable policies to guide day-to-day behavior. The result is predictable – inconsistent practices, potential security exposure, and a growing volume of low-quality AI-generated output. A practical AI use policy provides guardrails that enable teams to move quickly without risking the business.
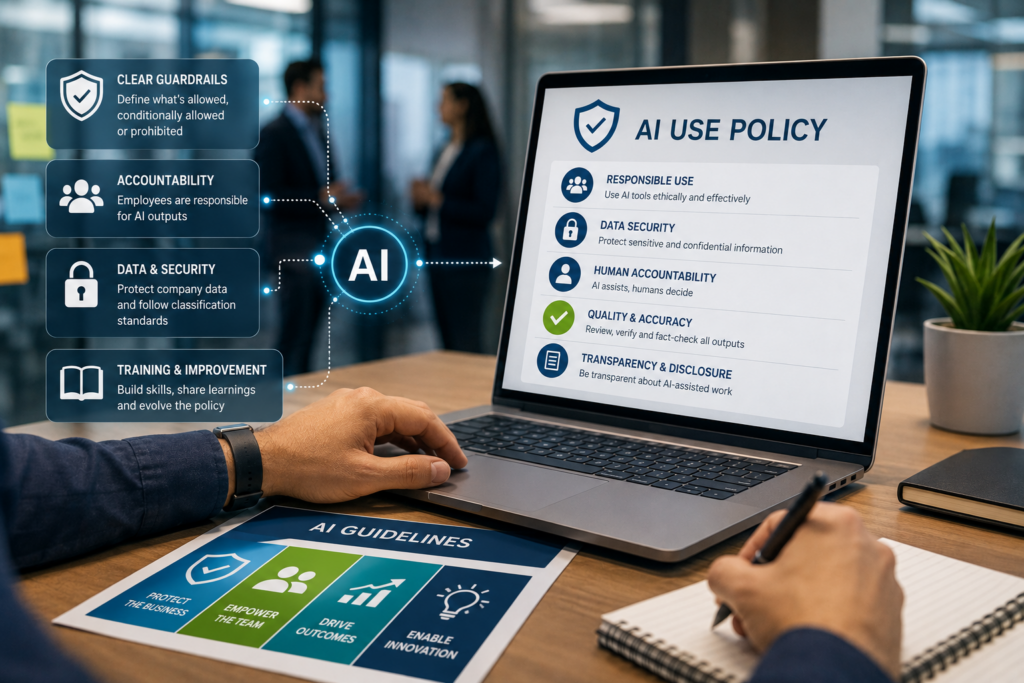
Start with clear definitions and scope. “AI” should include large language models, embedded SaaS features, internal agents, and any third-party service that processes company data. From there, define where AI is allowed, conditionally allowed, or prohibited. For example, drafting internal communications or summarizing non-sensitive content may be acceptable, while using AI with regulated data, customer PII, or confidential commercial terms should be restricted to approved, governed platforms.
Accountability is the cornerstone of an effective policy. AI outputs must be treated as suggestions, not decisions. Employees remain responsible for anything they submit or approve. Require users to review, edit, and fact-check all AI-generated content before sharing. Discourage “AI dumping,” where unedited outputs are pasted into emails, reports, or RFP responses. For higher-risk activities, establish human-in-the-loop checkpoints so qualified reviewers validate outputs before external communication or system changes.
Data handling and security require explicit guidance. Define what data can be entered into AI tools and which systems are approved for use. Reinforce data classification standards, including when to redact sensitive information. Where appropriate, require logging or audit trails for AI-assisted activities so decisions can be traced and reviewed if issues arise.
Finally, invest in training and continuous improvement. Provide practical instruction on effective prompting, recognizing weak or incorrect outputs, and applying policy in real scenarios. Encourage teams to share both successful use cases and failures. This feedback loop helps refine the policy as tools evolve and new risks emerge.
A well-designed AI use policy is not just a compliance document. It is an operational tool that aligns teams, protects the organization, and enables responsible innovation at scale.
Ready to take the next step? Explore how the AOTMP® TEM Performance & Value Alignment Program helps organizations benchmark, optimize, and elevate their technology management outcomes. Learn more or enquire now →